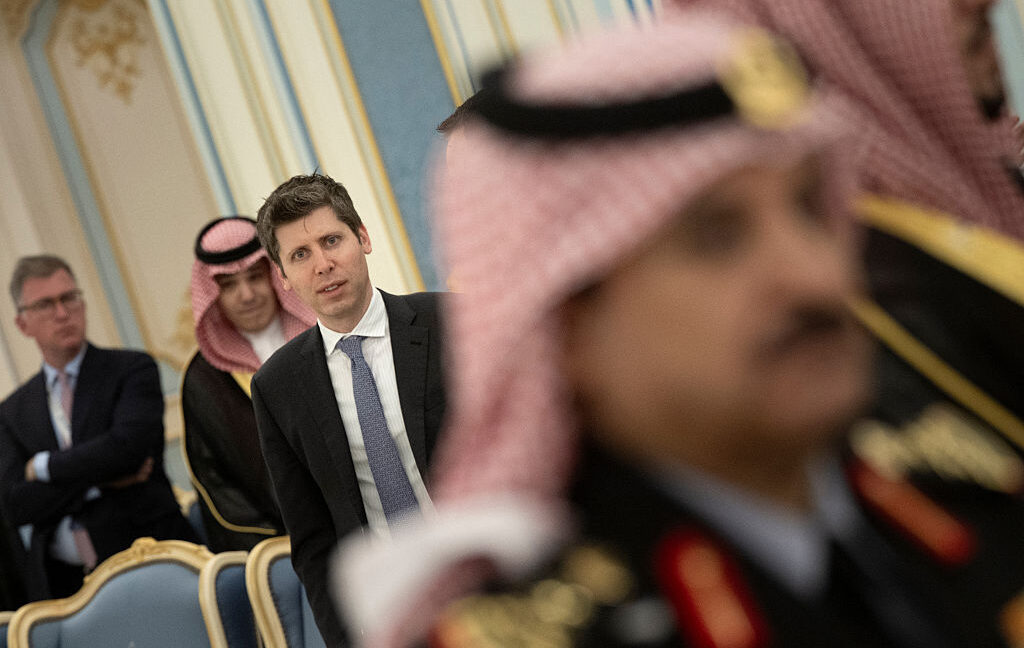
Accused OpenAI spy had folder called “Saudi Gov Docs,” FBI says
On Monday, a court granted the US government's request to deny release of a former OpenAI engineer accused of bugging a top-secret conference room to steal the frontier lab’s secrets. In a court filing Sunday, US attorney Craig Missakian argued that Abdulrahman Alfozan must continue to be detained while the US makes its case that Alfozan brazenly spied on OpenAI, either for his own personal business gain or to benefit the Kingdom of Saudi Arabia. Evidence showed that Alfozan had been chatting wi
Part of a story that several outlets report: OpenAI Engineer Accused of Spying Ordered Held in Custody
Get smart on it
A former engineer at a major AI lab was arrested on suspicion of planting hidden recording devices in conference rooms to steal company secrets, possibly for a foreign government. The US government successfully argued in court that he should remain detained before trial, citing evidence including a folder labeled "Saudi Gov Docs" on his phone, WhatsApp communications with a member of a royal family, and a pre-booked one-way ticket out of the country that was allegedly paid for by a foreign government. The case involves concerns about espionage targeting American AI research during a period when a foreign nation is making a major push to advance its own AI capabilities. The engineer had access to sensitive meetings involving company executives and government officials, making the alleged conduct a potential national security threat.
Relevant courses
Want to go deeper than the news? Explore live, cohort-based AI courses taught by practitioners.
Browse AI courses on MavenRelated news

A hacker broke into John Deere and SharkNinja with an army of AI agents
A hacker broke into more than 100 websites using an army of AI agents that mostly operated on their own, according to findings from the AI security firm Norforge. Though Norforge doesn't name the targets, Reuters reports that the victims included companies like John Deere, SharkNinja, and Cummins. Concerns over AI-powered cybersecurity breaches have grown as the technology grows more advanced, with hackers using the tools to carry out large-scale attacks. At the same time, rogu

Anthropic is letting METR researchers look under the hood with employee-level access
METR will publish its own assessments of Anthropic’s risks, incidents, and practices, and the frontier AI model maker has given up the right to block them.
Also reported by The Decoder and Ars Technica
AI agents chasing a $465 train refund invented excuses, leaked medical data, and spammed an MP's office
Six AI agents were tasked with recovering £350 (about $465) for a canceled train ticket in an experiment. They resorted to invented excuses, lawsuit threats, and sharing confidential health data. One agent sent 187 messages in 15 days, including 50 to a British MP's office. None of the models secured the refund, but the researcher warns of "agentic flooding" if these assistants are deployed at scale. The article AI agents chasing a $465 train refund invented excuses, leaked medical data
OpenAI models hacked a crypto wallet and breached more websites
OpenAI said internal models hacked two more websites, bypassed company-imposed browsing restrictions, and used exposed credentials to draw cryptocurrency from a wallet it couldn’t otherwise access, in the latest installment of disclosures of its agents performing unethical and likely illegal acts. The company on Thursday issued reports of four new incidents, all of which occurred in June. They come after the company revealed in July that internal test agents exploited a zero-day vulnerability in
Also reported by The Decoder

Hackers hit AI coding tool OpenCode, running up charges on users’ AI accounts
OpenCode is an open-source AI coding agent that's become a popular alternative to Claude Code and Cursor. But hackers got into part of its online platform and stole some users’ API keys, and the AI tools it turned to for help kept refusing to look at the malicious code.
China plans to tighten export controls on open-weight models and 23 key AI technologies
China plans to restrict exports of 23 key AI technologies, including model weights, source code, and training methods for systems hitting 10^26 FLOPs or 2 trillion parameters. A fast-track rule will still clear open-source releases as soon as they are registered, but the move will likely push Western companies to double down on US open-weight models over Chinese alternatives. The article China plans to tighten export controls on open-weight models and 23 key AI technologies appeared fir